Speaking

I wrote From Heatmaps to Histograms and built the cyber risk quantification program at Netflix. Since 2014 I’ve given about 70 talks, workshops and panels. Most are about measuring cyber risk in dollars: how to start a program, where the data comes from, what AI changes, and how to explain a range of possible losses to the people who have to act on it.
I’ve spoken at RSA Conference in five different years, at DEF CON, FAIRcon and SiRAcon, at several BSides and ISACA conferences, and at FAIR Institute chapters around the country. Several of my recent sessions work through a live analysis, and the workshops are hands-on.
I speak at conferences and at corporate and private events, including leadership offsites and team meetings. I’m happy to sign books at your event, and Springer offers bulk pricing if you’d like copies for your attendees.
What I talk about
Nearly everything I talk about comes back to one idea: cyber risk is measurable, and the belief that it isn’t is something our industry inherited and never tested. These are the topics I’m asked about most.
- From Heatmaps to Histograms, my signature keynote on why risk matrices fail and what to use instead
- Finding, vetting, and blending the data a risk analysis needs, even when you think you have none
- Running a first quantitative risk analysis with a spreadsheet and no statistics degree
- Talking about cyber risk with boards and executives in dollars
- Deciding how much security is enough, and what the budget is buying
- Measuring AI risk in dollars and probabilities
- Using generative AI in risk analysis, and where it still needs a human check
- Calibration, and how to get good estimates out of experts
- How bad statistics spread through the security industry, and how to grade a report
- Security metrics and KRIs that inform decisions
- The economics of ransomware
- Building a risk quantification program that lasts past its first year
- The six levers that change cyber risk, of which controls are only one
Any of these can run as a keynote, a workshop, a fireside chat or a debate. Tell me what your audience is wrestling with and I’ll tell you what I’d bring. If your team wants to practice the methods together, I also run private workshops, and the book site describes the formats.
Watch a talk
Program chairs usually want to see a talk before booking one. These recordings are free to watch.
- Escaping the Security Treadmill: A Better Way to Show Risk, Qualys Cyber Risk Series, 2025
- Quantifying in the Age of Hallucination, SiRAcon ’25, on SiRA’s free recordings page
- A video interview on the GRC Engineer podcast with Ayoub Fandi, 2025
- Baby Steps: Easing Your Company into a Quantitative Cyber Risk Program, SIRAcon ’21
- Case Study: How FAIR Analyses Support Decision-Making at Netflix, FAIRCON 2020
- Incentivizing Better Risk Decisions: Lessons from Rogue Actuaries, SIRA webinar, 2019
- Crowdsourced Probability Estimates: A Field Guide, SIRAcon 2018
Recent talks
Beyond Heatmaps: Hands-On Cyber Risk Quantification with FAIR
Did We Solve the Data Problem? Judgment, Beliefs, and Risk in the AI Age
The Future of Cyber Risk Intelligence
The Six Levers That Actually Move Risk (Hint: It’s Not Just Controls)
Speaking the Language of Business: Cyber Risk Reimagined
Quantifying in the Age of Hallucination: How I Learned to Stop Worrying and Trust the AI (Sometimes)
Talks, panels and webinars since 2014
Titles with a link have a recording you can watch.
2026
- A panel on qualitative and quantitative risk analysis (ERQI Global Virtual Risk Summit, online)
- Beyond the Heat Map: An Introduction to FAIR for Security Teams (ISACA Sacramento Flagship Conference)
- A session on using a finished risk analysis to make a decision (The Quantify Workshop, Salt Lake City)
- The Woozle effect: how unsourced numbers sink good risk analysis (SiRA webinar)
- Beyond Heatmaps: Hands-On Cyber Risk Quantification with FAIR (workshop, DEF CON 34 Noob Village, Las Vegas)
- After the Monte Carlo: Communicating Quantitative Risk to Executives (FAIR Institute Dallas-Fort Worth chapter, online)
- Did We Solve the Data Problem? Judgment, Beliefs, and Risk in the AI Age (FAIR Institute Northern California chapter, Sunnyvale)
- From Heatmaps to Histograms: Getting Started with FAIR (FAIR Institute Upper Midwest chapter, online)
- Did We Solve the Data Problem? Judgment, Beliefs, and Risk in the AI Age (keynote, SiRAcon ’26, Boston)
- Use Cases Using AI for Cyber Risk Quantification (FAIR Institute webinar with Ostrich Cyber-Risk)
- The Future of Cyber Risk Intelligence (FAIR Institute seminar, RSAC 2026, San Francisco)
- Six Forces That Move Your Risk (Whether You’re Watching or Not) (SiRA webinar)
- Escaping the Security Treadmill: A Better Way to Show Risk (FAIR Institute Sunshine State chapter, online)
- From Gut Feel to Good Data: How AI Can (and Can’t) Transform Risk Management (FAIR Institute webinar)
- The Six Levers That Actually Move Risk (FAIR Institute Greater Ohio chapter, online)
2025
- Why Tech Companies Need Risk Quantification (FAIR Institute webinar with Ostrich Cyber-Risk)
- The Six Levers That Actually Move Risk (Hint: It’s Not Just Controls) (FAIRCON25, New York)
- Case Study: Operationalizing Decision Support in the Age of AI (with Zach Cossairt, FAIRCON25, New York)
- Change Management: The Mental Shifts That Make Quantification Stick (workshop, Risk Awareness Week, online)
- Speaking the Language of Business: Cyber Risk Reimagined (panel, Qualys ROCon Americas, Houston)
- From Gut Feel to Good Data: How AI will Transform Risk Management (Qualys ROCon Americas, Houston)
- Heatmaps belong in museums: Debunking common myths about CRQ (Citalid webinar)
- From Gut Feel to Good Data: How AI Can (and Can’t) Transform Risk Management (SF ISACA Fall Conference, San Francisco)
- Escaping the Security Treadmill: A Better Way to Show Risk (Qualys Cyber Risk Series, online)
- Quantifying in the Age of Hallucination: How I Learned to Stop Worrying and Trust the AI (Sometimes) (SiRAcon ’25, Boston)
- A walk through a FAIR analysis (FAIR Institute seminar, RSAC 2025, San Francisco)
2024
- Risk Journey (panel, SiRAcon ’24, Boston)
2022
- Case Study: Five Objections to FAIR and How to Overcome Them (with Prashanthi Koutha, FAIRCON22, Washington, DC)
- The Essentials of Risk Scenarios (with Lisa Young and Evan Wheeler, ISACA Virtual Summit)
- Why is FAIR worth it for organizations? A Fireside Chat with FAIR Institute Members (FAIR Institute seminar, RSA Conference 2022, San Francisco)
- Asking the Right Questions: A Workshop Designed to Quantify Intangibles in Cyber Risk Analysis (with Apolonio Garcia and Michael Radigan, SIRA webinar)
- How do I get started? Easing your company into a quantitative cyber risk program (i-4 Global Hybrid Forum, online)
2021
- Fireside Chat: How to Get a FAIR Program Off the Ground (with Prashanthi Koutha, FAIRCON21, online)
- Rethinking Cyber Risk Responses (workshop, Risk Awareness Week, online)
- Joint Roundtable on Cyber Risk Quantification (with Jack Jones and Evan Wheeler, ISACA Virtual Summit)
- Operational Risk: Lessons in Resilience and Quantification (panel, CIISec LIVE, online)
- Common Use Cases of FAIR Analysis (FAIR Institute beginner chapter meeting, online)
- Baby Steps: Easing Your Company into a Quantitative Cyber Risk Program (SIRAcon ’21, online)
- Communicating Quantitative Risk Results to the Board (with Lisa Young and Vince Schira, SIRA webinar)
- Innovation Webinar 11: Cyber and Operational Risk (with Richard Seiersen, CIISec webinar)
- Rethinking Risk Response (ISACA webinar)
- Practical Implications of Managing Cyber Risk in Financial Terms (panel, PRMIA Cyber Risk Forum, online)
- Building and Running a Quantitative Risk Management Program: Lessons from the Field (panel, ISSA Central Ohio InfoSec Summit, online)
- Incentivizing Better Risk Decisions: Lessons from Rogue Actuaries (FAIR Institute Ohio chapter, online)
- Navigating Cyber Risk Quantification (panel, GRC Leadership Series, online)
2020
- Case Study: How FAIR Analyses Support Decision-Making at Netflix (FAIRCON 2020, online)
- Scaling a FAIR-Based Cyber Risk Management Program at Netflix (with Joe Vinck, RiskLens webinar)
- Expert Estimation for Risk Analysis: A Debate (panel I moderated, SIRAcon 2020, online)
- Breach Impacts: How to Estimate Costs More Accurately (panel, Advisen webinar with the Cyentia Institute)
2019
- Incentivizing Better Cyber Risk Decisions: Lessons from Rogue Actuaries (evening talk hosted by Airbnb, San Francisco)
- Incentivizing Better Risk Decisions: Lessons from Rogue Actuaries (SIRA webinar)
- Incentivizing Better Risk Decisions: Lessons from Rogue Actuaries (SIRAcon 2019, Cincinnati)
- Expert Estimation and Calibration Training (workshop, SIRAcon 2019, Cincinnati)
- Getting Started with a Quantitative Cyber-Risk Program (Peer2Peer discussion, RSA Conference 2019, San Francisco)
2018
- How to Lie with Statistics, Information Security Edition (CircleCityCon 5.0, Indianapolis)
- Crowdsourced Probability Estimates for Cyber Risk Analysis (FAIR Institute webinar)
- Quantitative Information Security Risk Management (Birds of a Feather discussion, RSA Conference 2018, San Francisco)
- Issues of Quantifying Risk around Identity and Access Management (IAM) (panel, RSA Conference 2018, San Francisco)
- Becoming a security bookie: Improving your estimations with calibration (Peerlyst Live, San Francisco)
- A panel on quantitative risk analysis with FAIR (FAIR Institute breakfast during RSA week, San Francisco)
- Cybersecurity Aspects of Blockchain and Cryptocurrency (PRMIA round table, San Francisco)
- Crowdsourced Probability Estimates: A Field Guide (SIRAcon 2018, Seattle)
2017
- Should I Pay or Should I Go? Game Theory and Ransomware (BSides San Francisco)
2016
- Ransomware & Game Theory: To Pay, or Not to Pay? (NBTcon 3, San Francisco)
- Cyber Attack Analysis with FAIR (FAIR Institute SF Bay chapter, San Jose)
- Measuring DDoS Risk Using FAIR (the first FAIRcon, Charlotte)
- Can Cyber Extortion Happen to You? Practical Tools for Assessing the Threat (BSides Seattle)
2015
- How to Lie with Statistics, Information Security Edition (BSides San Francisco)
- Case Study: eGift Card Fraud (U.S. Secret Service Electronic Crimes Task Force, San Francisco)
2014
- How to Improve Your Risk Assessments with Attacker-Centric Threat Modeling (SF ISACA Fall Conference, San Francisco)
Podcasts
- Zero Trusts Given with Ben Rothke, 2026, an interview about the book
- The Watchtower with Ash Hunt, 2026, on why AI doesn’t give us judgment
- Risk Is Our Business with Michael Rasmussen, 2026, an hour on the book
- Alice in Supply Chains with Adrian Sanabria and Alexandre Sieira, 2026, on cyber risk quantification
- Security & GRC Decoded with Raj Krishnamurthy, 2025, on data-driven decisions for CISOs
- CISO Confidential with Saket Modi, 2025, on the human side of breach response
- Risk Is Our Business with Michael Rasmussen, 2025, heatmaps, histograms, and star charts
- GRC Engineer with Ayoub Fandi, 2025, on quantification as a mindset shift for GRC
- GRC & Me with Chris Clarke, 2023, on moving from colored charts to quantification
- GRC & Me with Megan Phee, 2022, on kickstarting risk management with quantification
- ISACA Podcast with Paul Phillips, Jack Jones and Evan Wheeler, 2021, on getting started with risk quantification
- The Resilient Lawyer with Jeena Cho, 2015, on data security
In the press
These are some of the reviews of my book and some of the articles that interview or quote me. My own articles and chapters are on the Publications page.
- RSAC Conference blog, Ben Rothke, 2026, a Book of the Month review
- GRC Report, Michael Rasmussen, 2026, a review of the book
- IB Magazine, Nicole van Deursen, 2026, a review of the book in Dutch
- Rick’s First Principles Newsletter, Rick Howard, 2026, on the book and its nomination for the Cybersecurity Canon Hall of Fame
- TechTarget, Mary K. Pratt, 2026, on quantifying cyber risk at Netflix
- CSO Online, Deb Radcliff, 2025, on LLM hype versus reality for CISOs
- Dark Reading, Kelly Sheridan, 2020, on how Netflix makes security decisions
- Dark Reading, Curtis Franklin, 2018, on how to start a risk assessment
- The Wall Street Journal, Kim S. Nash, 2016, on blockchain
- CSO Online, Mary Brandel, 2016, on becoming a security pro
- Global News, Sean O’Shea, 2016, on gift card fraud
Speaker kit
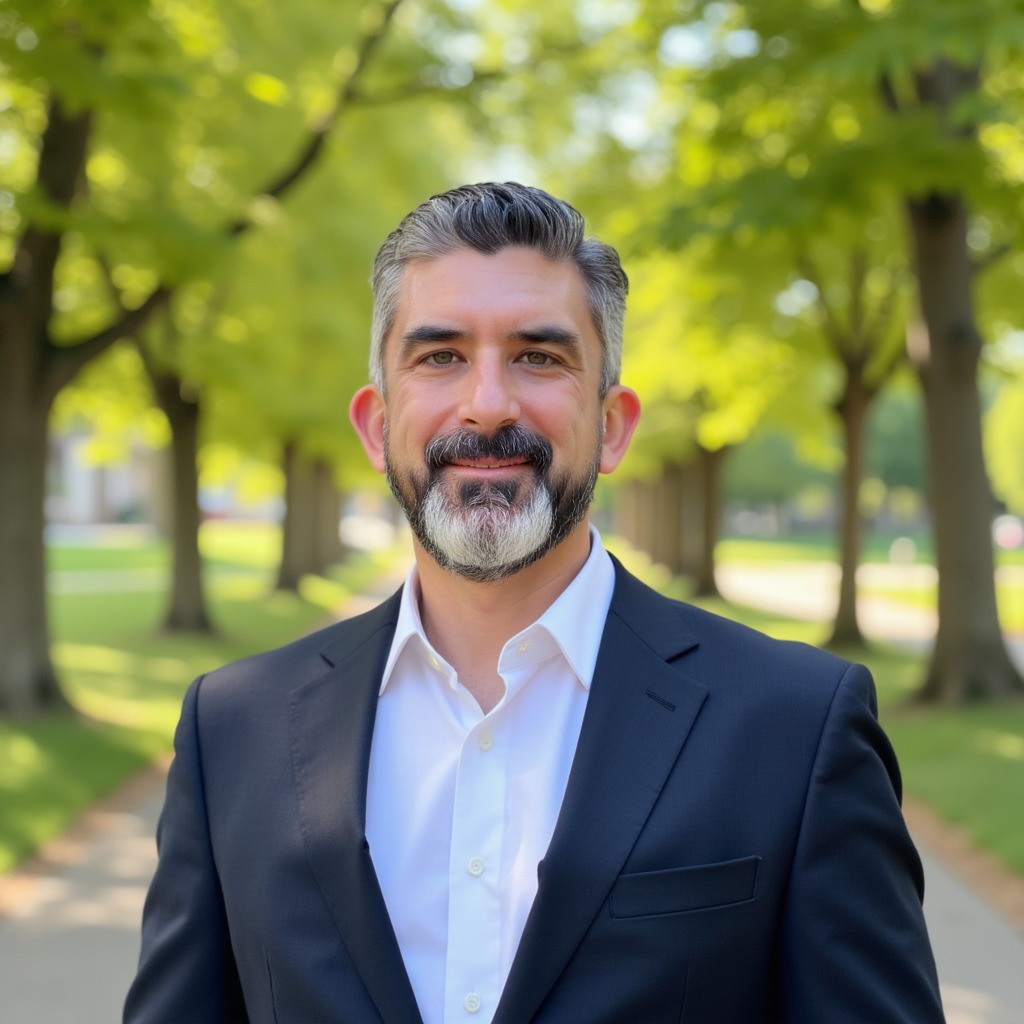
Organizers usually ask for a bio and a photo, so both are here to copy or download. The speaker kit puts both bios, my topics and a headshot on one page.
Short bio
Tony Martin-Vegue has worked in security and risk for more than 25 years. He built the cyber risk quantification program at Netflix, wrote From Heatmaps to Histograms (Apress, 2026) and started CRQ Bootcamp, which teaches risk quantification in live classes. Through his firm, 95 Risk Advisory, he helps companies build programs of their own.
Long bio
Tony Martin-Vegue has worked in security and risk for more than 25 years. He spent six years at Netflix, where he built and led the company’s cyber risk quantification program, and in 2025 he founded 95 Risk Advisory to help other companies build their own. Recent clients include some of the biggest companies in AI and finance.
He wrote From Heatmaps to Histograms: A Practical Guide to Cyber Risk Quantification (Apress, 2026), a book for anyone who wants to start measuring cyber risk in dollars. He also started CRQ Bootcamp, where he and Apolonio Garcia teach the book’s methods in live classes. He chairs the FAIR Institute’s San Francisco chapter, and the Institute gave him its FAIR Ambassador Award in 2020. He’s an Executive Fellow at the Cyentia Institute and a contributor to the 2026 Verizon Data Breach Investigations Report.
He has spoken at RSA Conference, DEF CON, FAIRcon and SiRAcon, and at several BSides and ISACA conferences. He lives in the San Francisco Bay Area.
Downloads
- Speaker kit PDF, one page
- Headshot JPG, 1024 by 1024 pixels
- On stage at Qualys ROCon JPG, 3000 by 2000 pixels

To book a talk, send me a note through the contact page with the event, the date, the audience and the format you have in mind.